Nov 13: As businesses become increasingly digital, one question is becoming central to enterprise security: how can organisations ensure that the right people and devices have access to the right information without exposing their systems to cyber threats? For decades, passwords have been the primary method of digital authentication. However, with phishing, stolen credentials, remote working and cloud-based operations becoming more common, traditional password-based security is increasingly proving inadequate.
This is driving a major transformation in enterprise IT. Organisations are moving towards passwordless authentication, using technologies such as passkeys, biometrics, security keys and device-based verification to establish digital identities. At the same time, identity security is becoming a strategic priority, shifting cybersecurity from simply protecting networks to verifying every user, device and application accessing business resources.
This change is more than a technological upgrade. It represents a new approach to business security, operational efficiency and digital trust. For both the UK and India, where digital services, financial transactions and enterprise technology are expanding rapidly, secure digital identity will play an increasingly important role in supporting future growth.
Understanding Digital Identity and Passwordless Authentication
Digital identity refers to the information and credentials used to establish and verify the identity of an individual, device or application accessing a digital system. Within an enterprise, it determines who can access business applications, company networks, cloud platforms, databases and sensitive information.
Traditionally, organisations have relied on usernames and passwords. However, passwords can be weak, reused across multiple accounts, stolen through phishing or exposed during data breaches.
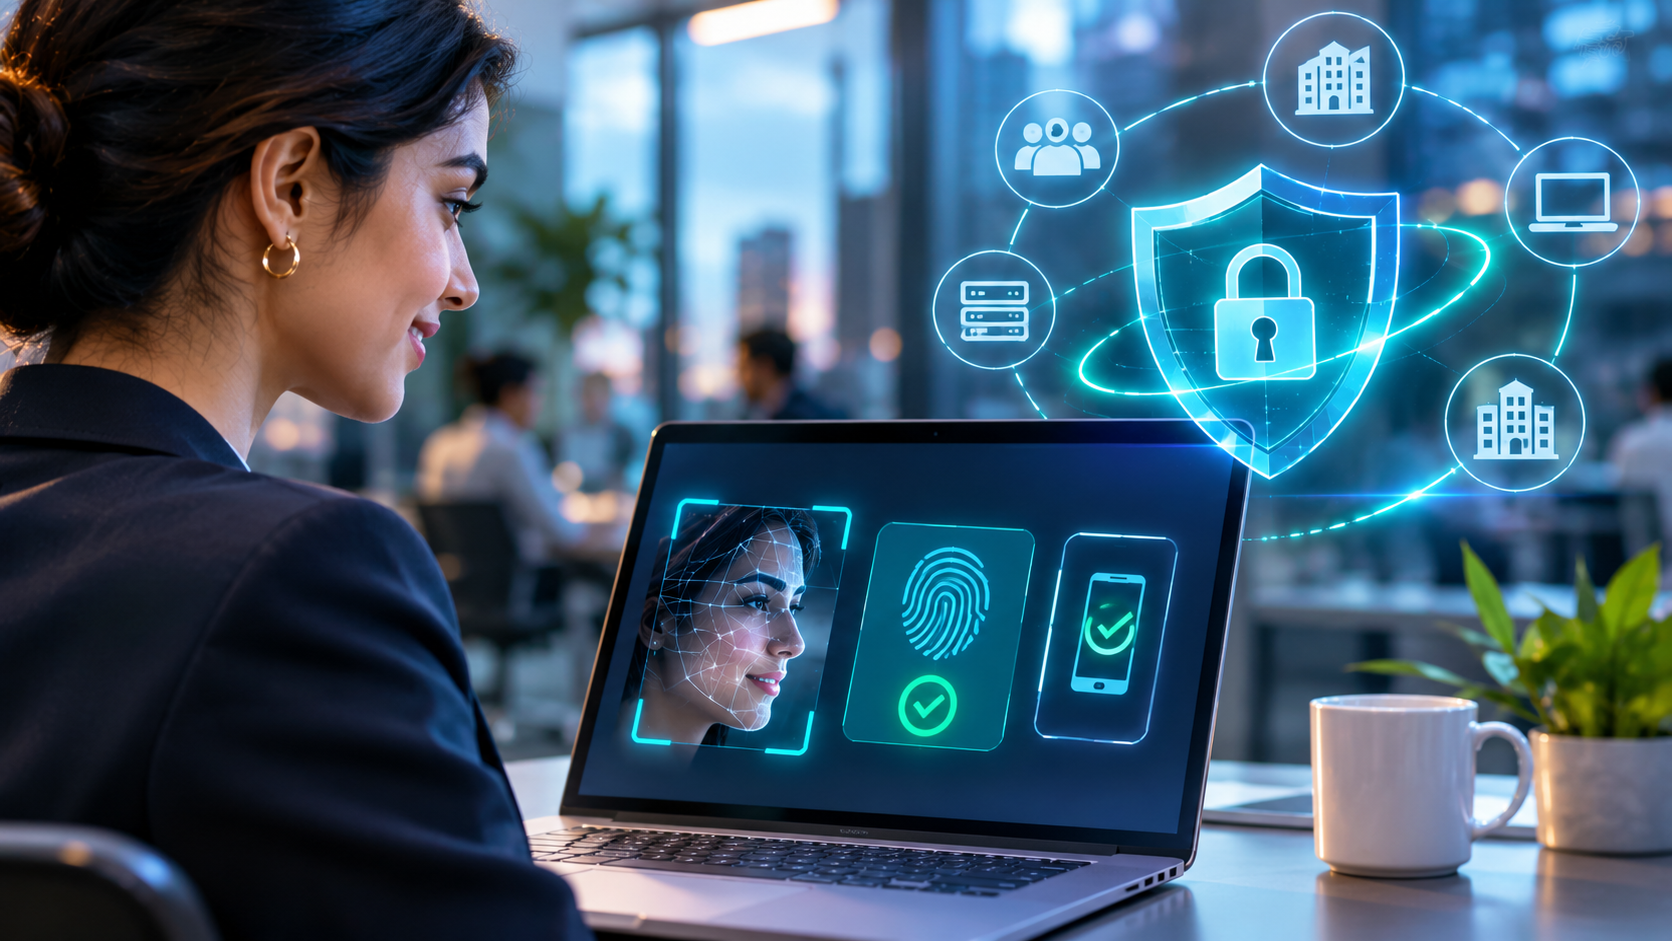
Passwordless authentication offers an alternative by allowing users to access systems without entering a traditional password. It uses technologies such as:
- Biometric authentication: Fingerprint or facial recognition to verify a user’s identity.
- Passkeys: Cryptographic credentials stored on trusted devices, allowing users to authenticate without sharing a password.
- FIDO2 security keys: Physical authentication devices that provide strong protection against phishing.
- Device-based authentication: Verification based on trusted devices and their security status.
- Smart cards and digital certificates: Cryptographic credentials used to authenticate users and devices.
An important distinction is that biometric information often unlocks a credential stored securely on a device rather than being transmitted as a password. This helps make modern passwordless authentication more secure.
Why Businesses Are Moving Beyond Traditional Passwords
The expansion of cloud computing, remote working, digital transactions and interconnected business applications has increased the number of identities that organisations must protect.
Employees may access company systems from different locations, while customers, suppliers, contractors and automated applications also require controlled access. A compromised account can therefore expose sensitive business information, disrupt operations and damage customer confidence.
The UK’s Cyber Security Breaches Survey 2025/26 reported that 43% of businesses experienced a cyber breach or attack during the previous 12 months, with phishing affecting 38% of businesses. This highlights the continuing challenge of protecting digital access and organisational information.
For businesses, the shift towards passwordless authentication is being driven by three important priorities:
- Reducing cyber risks: Strong authentication methods can make phishing, credential theft and unauthorised account access more difficult.
- Lowering operational costs: Password resets, account lockouts and access-related support requests consume IT resources. Reducing password dependence can help lower this administrative burden.
- Improving productivity: Faster and simpler authentication allows employees to access business applications with less friction, particularly in organisations managing multiple systems.
The business case is therefore not limited to cybersecurity. It also involves reducing operational overheads, improving employee experience and protecting business continuity.
The Relationship Between Passwordless Authentication and Identity Security
Although closely connected, passwordless authentication and identity security serve different purposes.
Passwordless authentication focuses on how a user proves their identity when accessing a system. Identity security is broader, covering identity verification, access permissions, authentication, monitoring and the management of user and device access throughout their lifecycle.
For example, when an employee accesses a company’s financial platform, a passkey may verify their identity. The organisation’s identity security framework then determines whether that employee is authorised to access financial information, whether the device is trusted and whether additional verification is necessary.
This creates a more comprehensive approach to access management. Instead of relying only on passwords or a single login event, organisations can evaluate identity, permissions and security conditions throughout the access process.
FIDO2, Passkeys and Adaptive Security: The Technologies Driving Change
Several technologies are shaping the future of digital identity.
FIDO2 and passkeys
FIDO2 is an authentication standard that supports passwordless and phishing-resistant sign-in. Passkeys use public-key cryptography, meaning authentication relies on a pair of cryptographic keys rather than a shared password. The private key remains protected on the user’s device, while the corresponding public key is used by the service to verify authentication.
This makes passkeys more resistant to phishing because they are designed to work with the legitimate website or application for which they were created.
Adaptive and context-based authentication
Modern security systems increasingly consider the context of an access request. Factors such as device health, location, login behaviour and the sensitivity of the requested information can help determine whether additional verification is required.
For example, an employee accessing routine documents from a recognised device may experience a straightforward login process, while an unusual attempt to access sensitive financial records may trigger additional security checks.
Multi-factor authentication
Passwordless authentication can work alongside multi-factor authentication, providing additional protection through different verification factors. The focus is increasingly on phishing-resistant methods rather than simply adding more login steps.
Identity lifecycle management
Organisations must also manage identities throughout their lifecycle, from employee onboarding and access allocation to role changes and account deactivation. This is particularly important as businesses increasingly rely on contractors, external partners, software applications and automated systems.
Zero Trust: A New Foundation for Enterprise Security
Another major development supporting this transformation is the Zero Trust security model.
Traditional IT security often assumed that users operating within a company’s internal network could be trusted. However, modern enterprises operate across cloud platforms, remote locations and multiple devices, making network-based trust insufficient.
Zero Trust follows a simple principle: never automatically trust a user or device simply because it has previously accessed a system. Every access request must be evaluated according to identity, permissions, device security and organisational policies.
Its core principles include continuous verification, least-privilege access, device security, strong authentication and ongoing monitoring.
Passwordless authentication strengthens this approach by providing more secure ways to verify identities. Identity security ensures that access remains controlled, while Zero Trust provides the broader framework for making access decisions.
Together, these technologies can help organisations develop a more resilient security environment.
Business Applications Across Industries
The importance of digital identity extends well beyond corporate login systems. It is becoming essential across industries that depend on secure digital transactions and sensitive information.
- Banking and financial services: Passkeys, biometrics and device verification can protect digital accounts, financial transactions and customer information.
- Healthcare: Secure identity management can protect electronic medical records and ensure that authorised healthcare professionals have appropriate access to patient information.
- Government services: Digital identity systems can support secure access to public services, official records and online applications.
- Retail and e-commerce: Passwordless authentication can simplify customer login processes while reducing account takeover risks.
- Manufacturing: Identity security can protect connected machinery, industrial control systems and operational technology.
- Cloud computing: Centralised identity controls can manage access across cloud applications, remote infrastructure and business data.
- Artificial intelligence: AI agents, automated applications and software systems require their own verified identities, controlled permissions and continuous monitoring.
The growing use of AI agents is particularly significant. As automated systems begin performing tasks on behalf of employees and organisations, businesses must ensure that these digital identities have clearly defined permissions and cannot access information beyond their authorised responsibilities.
India’s Opportunity in the Digital Identity Transformation
India presents an important opportunity in the evolution of digital identity. The country’s expanding digital economy, growing fintech ecosystem, widespread adoption of online services and developing technology sector are increasing the need for secure and reliable authentication.
Digital public infrastructure, including Aadhaar-based identity services and UPI-enabled payments, has helped establish a large-scale environment for digital interactions. As businesses expand online banking, e-commerce, digital lending, healthcare services and enterprise platforms, protecting user identities becomes increasingly important.
For Indian enterprises, passwordless authentication could help reduce account-related risks, simplify employee access and improve customer experiences. Banks and financial institutions can strengthen digital access, while healthcare providers can improve the protection of sensitive records. Technology-driven businesses can also use identity security to manage employees, customers, suppliers and automated applications across interconnected systems.
India also has opportunities beyond domestic adoption:
- IT and cybersecurity services: Indian technology providers can develop identity management, authentication and security solutions for international markets.
- Global business partnerships: Collaboration with international organisations can support research, technical development and secure authentication standards.
- Digital financial services: Stronger authentication can help protect online transactions and reduce the risks associated with account compromise.
- Enterprise transformation: Businesses can modernise access management as they adopt cloud computing, automation and AI-driven operations.
- Skilled employment: Growing demand for identity security can create opportunities in cybersecurity, digital infrastructure, software development and technology consulting.
However, India’s digital identity expansion must also address privacy, data protection, accessibility and the risks of digital exclusion. Strong authentication should make services more secure without creating unnecessary barriers for users.
Challenges in Adopting a Passwordless Future
Despite its advantages, moving away from passwords requires careful planning. Many organisations still operate older applications and systems that may not support modern authentication standards. Integrating new technologies with existing infrastructure can therefore be complex and costly.
Other challenges include device compatibility, employee training, secure account recovery and managing access across multiple platforms. Organisations must also ensure that alternative authentication methods do not create weaker security gaps if a user loses a device or cannot access biometric verification.
Privacy is another important consideration, particularly where biometric information is involved. Businesses must handle personal data responsibly and comply with applicable data protection regulations.
Most importantly, passwordless authentication is not a complete replacement for identity security. Organisations must continue to protect user sessions, manage permissions, monitor suspicious activities and regularly review access rights.
Conclusion: Building a More Secure and Connected Digital Future
The future of enterprise IT will increasingly depend on how effectively organisations manage and protect digital identities. As traditional passwords become less suitable for a highly connected business environment, passkeys, biometrics, FIDO2 authentication and Zero Trust principles are creating new possibilities for stronger and more efficient security.
For businesses in the UK and India, this transformation offers benefits beyond reducing cyber risks. It can improve employee productivity, simplify IT operations, strengthen customer confidence and support the expansion of digital services.
Looking ahead, the growing use of artificial intelligence, cloud platforms and automated systems will make identity security even more important. Organisations will need to verify not only people but also the devices, applications and AI agents operating within their digital environments.
Ultimately, the future of digital identity is not simply about eliminating passwords. It is about building a trusted digital ecosystem in which every access request is verified, every permission is controlled and security supports rather than slows business innovation. Organisations that recognise identity as a strategic business asset will be better prepared for the next generation of enterprise IT.